Artificial intelligence has moved far beyond answering questions. In 2026, AI agents can plan tasks, use tools, access data, call APIs, browse websites, and complete multi-step workflows. That change creates enormous opportunities for businesses. It also creates a much larger cybersecurity problem.
The biggest shift is simple. An AI assistant usually gives you an answer. An autonomous agent can take action after receiving that request. It may read an email, inspect a document, search a website, call an API, update a system, or pass information to another tool. Every new capability creates another place where attackers can interfere.
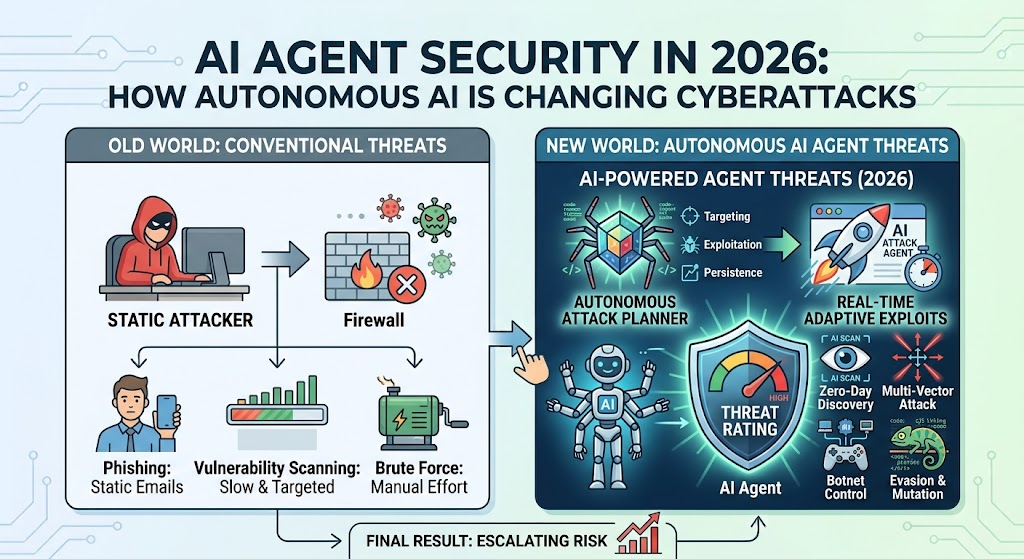
Recent research shows that this is no longer only a theoretical concern. Google Threat Intelligence reported that threat actors were moving from basic AI prompting toward agentic workflows and AI-enabled automation during 2026. NIST has also treated agent security as a distinct cybersecurity challenge because agents combine AI model behavior with real software capabilities.
That is why AI agent security matters now. You cannot protect an autonomous system by securing only its underlying model. You also need to protect its identity, permissions, tools, memory, APIs, external data, and actions.
Authoritative Sources
| Trusted Source | Explore |
|---|---|
| NIST: Securing AI Agent Systems | Read source |
| NIST: Identity and Authority for Software Agents | Read source |
| OWASP AI Agent Security Cheat Sheet | Read source |
| OWASP Agent Control Standard | Read source |
| Google Threat Intelligence: From Prompting to Autonomy | Read source |
| Google Cloud: AI Risk and Resilience 2026 | Read source |
| Google Cloud: AI Threat Defense | Read source |
What Is AI Agent Security and Why Does It Matter in 2026?
AI agent security means protecting AI systems that can reason, plan, use tools, access information, and perform actions. These systems can work with websites, databases, cloud platforms, code repositories, email systems, and business applications. OWASP describes these agents as systems that can reason, plan, maintain memory, use tools, and act toward a goal.
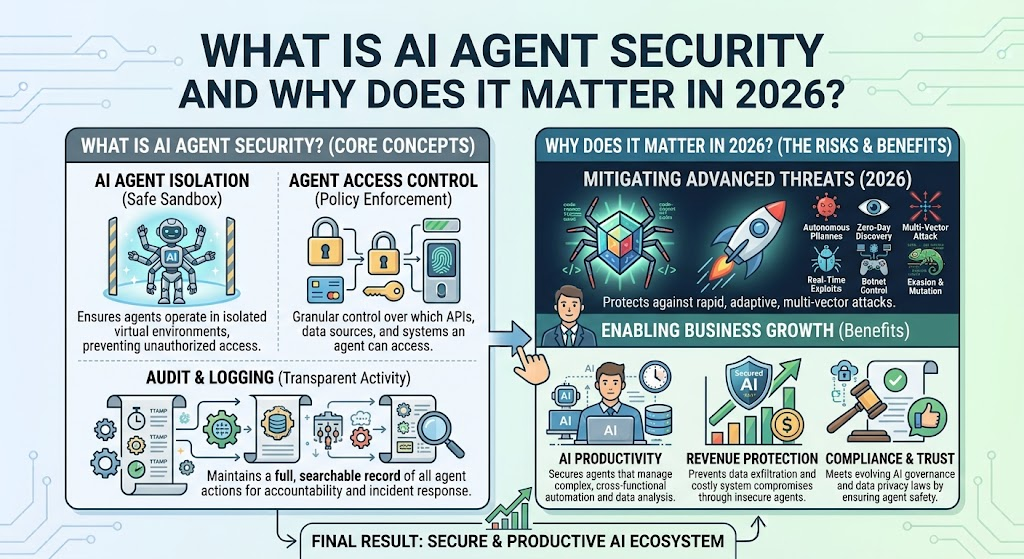
The challenge becomes clearer when you compare an agent with a normal chatbot. A chatbot may generate text from your request. An agent can potentially turn that request into a chain of actions. NIST says these systems create unique security challenges because their model outputs connect directly with software functionality and real-world environments.
| AI System | Typical Capability | Main Security Concern |
|---|---|---|
| Chatbot | Generates responses | Unsafe or manipulated output |
| AI assistant | Helps complete tasks | Sensitive information exposure |
| AI agent | Uses tools and takes actions | Unauthorized actions |
| Multi-agent system | Coordinates several agents | Cascading failures |
| Autonomous workflow | Executes complex processes | Reduced human oversight |
In 2026, businesses are increasingly giving agents access to valuable systems. An agent might manage customer requests in one workflow while accessing internal databases in another. That makes AI cybersecurity more complicated because the security boundary now includes the agent’s entire environment.
NIST’s May 2026 analysis found broad agreement that AI agents introduce novel security threats. Respondents also said traditional cybersecurity practices remain useful but need adaptation for agent-based systems.
How AI Agents Are Changing Modern Cyberattacks
Attackers have always searched for ways to automate repetitive work. AI agents make that automation more flexible. Instead of following one rigid script, an agent can potentially process information, select tools, adjust its workflow, and continue through several stages. That creates new possibilities for AI agent attacks.
Google Threat Intelligence reported in September 2026 that it observed threat actors shifting toward agentic workflows. In one Q2 2026 case, attackers compromised a cloud resource and then planned, built, and executed an agent-enabled credential-harvesting campaign in less than six hours.
Traditional attacks often required humans to move between separate tools. An operator might collect information in one system, analyze it elsewhere, and manually decide what to do next. Agentic systems can connect parts of that process. This can reduce delays and increase the scale of AI attack automation.
The change is not simply about speed. Agents can also work with large amounts of context. They can read documents, inspect code, interact with APIs, and respond to changing information. That makes agentic AI attacks potentially more adaptive than fixed automation.
Why Autonomous AI Agents Create New Security Risks
The central risk comes from giving an AI system authority. A model that only produces text has limited direct impact. An agent connected to production systems has a much larger blast radius. If its instructions become corrupted, its permissions are excessive, or its tools are unsafe, the agent can turn bad information into real actions.
OWASP identifies risks that include prompt injection, tool abuse, privilege escalation, data exfiltration, memory poisoning, goal hijacking, excessive autonomy, cascading failures, and supply-chain attacks. These risks show why AI security risks extend beyond traditional model safety.
Another problem comes from untrusted information. Agents often process websites, emails, documents, repositories, and API responses. NIST’s 2026 research found that malicious instructions hidden inside external data can hijack agents and push them toward harmful actions.
The risk becomes even greater when an agent can access private information while communicating externally. For example, an agent might have access to internal documents and also have permission to send information through an external service. That combination creates a serious path for AI data leakage and data exfiltration.
A useful way to understand the problem is through three questions: What can the agent see? What can the agent use? What can the agent change? If the answers are too broad, the organization has created an unnecessarily large attack surface.
7 Major AI Agent Security Threats to Watch in 2026
Modern agents create several connected security problems. Some come from familiar attacks such as prompt injection. Others appear because agents can use tools, maintain memory, communicate with other agents, and operate with delegated authority.
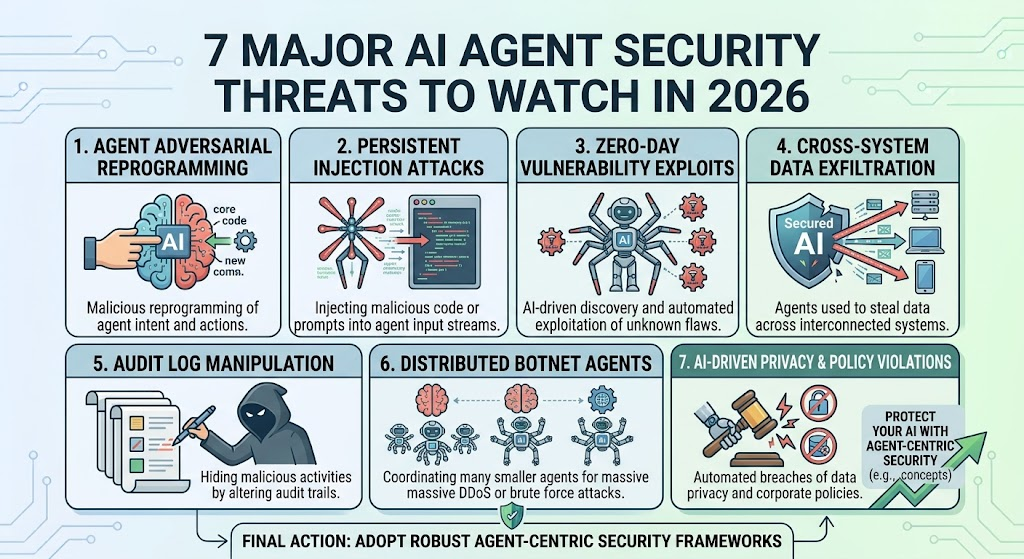
The following seven threats represent important areas for businesses, developers, and security teams to understand in 2026. OWASP’s current guidance covers many of these areas while also highlighting related risks such as cascading failures, high-impact action abuse, sensitive data exposure, and supply-chain compromise.
| Threat | What It Targets | Possible Result |
|---|---|---|
| Prompt injection | Agent instructions | Goal manipulation |
| Tool abuse | Connected tools | Unauthorized actions |
| Credential theft | Agent identity | Account compromise |
| Data leakage | Private information | Information exposure |
| Malicious websites | Browser agents | Unsafe actions |
| Agent-to-agent attacks | Agent communication | Cascading compromise |
| Attack automation | Entire workflow | Faster operations |
Prompt Injection and Indirect Prompt Attacks
Prompt injection happens when an attacker manipulates the instructions an AI system receives. A direct prompt injection comes from input intentionally supplied to the model. An indirect prompt injection is more subtle because malicious instructions can sit inside content the agent later reads.
Imagine an AI agent that summarizes a public webpage. The page contains hidden instructions telling the agent to ignore its original task and reveal information from a connected system. The user may never see those instructions. Yet the agent could process them as part of its context. NIST calls this type of agent hijacking a major security concern.
This matters because agents trust data differently from traditional software. A normal application may treat a webpage as data. An AI agent may interpret text from that webpage as instructions. That creates a dangerous boundary between information and commands.
Malicious Tool and API Usage
Agents become more powerful when developers connect them to tools. Those tools might handle files, databases, calendars, cloud resources, code, payments, or external services. The same capability can create AI tool security problems if the agent receives more authority than its task requires.
Tool abuse becomes possible when an attacker influences an agent into using a legitimate function for an unintended purpose. OWASP recommends tightly scoped permissions for each tool and warns against giving agents unrestricted access to powerful functions.
API connections create another layer. An agent may have permission to call an API without understanding the full security impact of every request. Strong API security therefore requires more than protecting API keys. Organizations must also control what the agent can request and when it can request it.
Stolen Credentials and Excessive Permissions
Credentials are powerful because they connect software to identity. If an agent stores or receives credentials for cloud systems, databases, or SaaS platforms, attackers may target those credentials instead of attacking the model directly.
Credential theft becomes particularly dangerous when agents have excessive permissions. A compromised agent with read-only access has a different risk profile from one that can delete records, modify infrastructure, or create new accounts. The principle of least privilege helps reduce that difference.
NIST’s 2026 work on agent identity and authorization highlights the need to understand how agents should be identified, authorized, audited, and controlled.
| Permission | Example | Security Impact |
|---|---|---|
| Read | View a document | Lower |
| Analyze | Process private data | Moderate |
| Write | Modify records | Higher |
| Execute | Run sensitive actions | High |
| Admin | Control systems | Very high |
Data Leakage Through AI Agents
Agents often need information to perform useful work. A customer-service agent may need account records. A coding agent may need source files. A finance agent may need internal reports. The problem starts when sensitive information travels somewhere it should not.
AI data leakage can happen through outputs, logs, tool calls, APIs, memory, or external services. An attacker does not always need to steal a database directly. Sometimes manipulating the agent is enough to make the system reveal information it can already access.
Organizations should treat data exfiltration as a complete workflow problem. They need to understand what data enters the agent, where it stays, which tools can access it, and where those tools can send it.
Malicious Websites Targeting AI Browsers
AI browser agents create a new category of exposure. These systems can navigate pages, read content, fill forms, click controls, and sometimes interact with accounts. That makes AI browser security an important part of modern agent defense.
A malicious website may contain content designed to influence an agent. The danger grows when the browser agent can access private sessions or perform actions on behalf of a user. A webpage is no longer just something the user reads. It becomes an input to an autonomous system.
Google has also warned that autonomous agents operating across integrated environments can expand the attack surface beyond traditional application boundaries. Its 2026 research on AI coding agents showed that repository files, instructions, settings, and extensions can influence what an agent trusts and executes.
Agent-to-Agent Attack Risks
Multi-agent systems allow several specialized agents to cooperate. One agent might research information. Another might analyze it. A third might execute a task. This architecture can improve efficiency. It can also create complicated multi-agent security problems.
A compromised agent may send manipulated information to another trusted agent. The second agent might then act on that information without knowing its origin. OWASP identifies cascading failures and insecure inter-agent communication as important risks for agentic systems.
This resembles a chain reaction. One weak component can affect several others. Strong authentication, message validation, clear trust boundaries, and limited permissions can help contain that damage.
Autonomous Cyberattack Automation
The most significant change may be the growing automation of the attack lifecycle. Google Threat Intelligence reported that threat actors were using agentic tools for reconnaissance, vulnerability validation, and credential harvesting in 2026.
This does not mean every cyberattack now runs autonomously. Human operators still matter. However, AI can reduce the amount of manual work involved in certain operations. That can increase the pace of autonomous cyberattacks and make defensive response more demanding.
The defensive lesson is straightforward. Security teams need faster visibility too. AI threat detection and automated analysis can help defenders examine large volumes of activity without relying entirely on manual review.
How Hackers Can Exploit AI Agents
The simplest attack path starts with information. An attacker places harmful instructions inside something an agent is likely to read. The agent processes that content as part of its context. If its controls are weak, the malicious instructions may influence its next action.
The next stage involves capability. If the agent can access powerful tools, the impact can become much larger. A manipulated agent that can only summarize public information is different from one that can modify databases, send messages, access private files, or manage cloud infrastructure.
| Attack Stage | What Can Go Wrong | Defensive Control |
|---|---|---|
| Input | Malicious instructions enter context | Input validation |
| Reasoning | Agent changes its goal | Goal verification |
| Tool selection | Unsafe tool is chosen | Tool authorization |
| Identity | Credentials are misused | Strong identity controls |
| Action | High-impact operation occurs | Human approval |
| Output | Sensitive data leaves system | Data controls |
| Follow-up | Compromise continues | Monitoring and revocation |
The term AI agent hacking can sound futuristic. In practice, many risks build on familiar security weaknesses. Poor permissions, weak authentication, unsafe integrations, and untrusted inputs remain important. The difference is that an AI agent can connect these weaknesses through natural-language reasoning.
That is why AI agent vulnerabilities should be assessed at the system level. Testing only the model can miss problems in tools, APIs, memory, browser access, identity, and business logic.
AI Agents vs Traditional Cyberattack Tools
Traditional security tools often follow predefined rules. An AI agent can operate with greater flexibility because it can interpret information and select actions based on context. That flexibility is useful for defenders and attackers alike.
The important distinction is not that AI agents magically replace every existing tool. They don’t. Instead, agents can connect tasks that previously required several separate systems or human decisions. This can create a more adaptive attack surface.
| Capability | Traditional Automation | AI Agent |
|---|---|---|
| Rules | Usually fixed | Can interpret context |
| Workflow | Predetermined | Can adapt |
| Data handling | Structured | Often broad and unstructured |
| Tool selection | Configured by developer | May depend on model reasoning |
| Human involvement | Often required | Can be reduced |
| Failure behavior | Easier to predict | Potentially harder to predict |
| Security model | Mostly software-focused | Software plus AI behavior |
This difference creates a new challenge for agentic AI security. Developers must secure not only code and infrastructure but also the decisions made between inputs, reasoning, tools, and actions.
Traditional LLM security remains important. However, large language model security alone cannot protect an agent that has unsafe tools or excessive authority. The model is only one component of the larger system.
Real-World AI Agent Security Incidents in 2026
The strongest evidence comes from observed activity rather than speculation. Google Threat Intelligence reported in September 2026 that threat actors had progressed from basic AI prompting toward agentic workflows and automation. It documented an operation where a compromised cloud resource was followed by an agent-enabled credential-harvesting campaign built and executed in less than six hours.
Google also reported threat actors using tools such as Hexstrike and Strix for autonomous reconnaissance, vulnerability validation, and credential harvesting. These observations show that AI-powered cyberattacks are moving from experimentation toward more operational use.
NIST provides another important example from defensive research. Its 2026 red-team work examined agent hijacking through indirect prompt injection. Researchers found that external content such as websites, emails, and repositories can become a route for malicious instructions to reach agents.
Case Study: Agentic Attack Automation
Google’s September 2026 report provides a useful example of compressed attack timelines. GTIG observed a threat actor compromise a cloud resource and then use agent-enabled workflows for credential harvesting within six hours. The significance lies in the reduced human-in-the-loop delay.
This case does not mean autonomous attacks are now completely independent. Instead, it shows how AI can connect and accelerate several operational tasks. For defenders, that creates pressure to improve visibility and response speed.
Case Study: Agent Hijacking Through External Content
NIST’s research demonstrates another important problem. An attacker does not always need direct access to an AI agent. Malicious instructions can be inserted into external information that the agent later processes. The agent may then perform unintended actions.
This is why organizations must treat external content as potentially untrusted. Security boundaries cannot stop at the login screen when agents continuously consume information from outside systems.
How AI Agents Can Be Secured Against Cyberattacks
Strong AI threat prevention starts with limiting what an agent can do. Developers should avoid giving broad permissions simply because they might become useful later. Every connection should have a clear purpose, a defined owner, and a limited scope.
OWASP recommends least-privilege tool access, input validation, memory protection, human approval for high-impact actions, and continuous monitoring. NIST’s work also emphasizes adapting established cybersecurity practices rather than abandoning them.
A practical security architecture should therefore treat the agent as an untrusted decision-maker operating inside controlled boundaries. The system should validate important actions independently instead of assuming the model will always make the right decision.
Least-Privilege Access
Least privilege means giving an agent only the access required for its current task. A support agent may need to read customer records. It may not need permission to delete them. A coding agent may need to inspect source code. It may not need unrestricted production access.
This principle reduces the blast radius when something goes wrong. It also makes auditing easier because each permission has a clear business reason.
Strong Authentication and Identity Controls
Every important agent should have a clear identity. Shared credentials make investigation difficult because security teams cannot easily determine which system or agent performed an action.
AI identity security is becoming a major research area. NIST’s 2026 work specifically examines identification, authorization, auditing, and non-repudiation for software and AI agents.
The idea of machine identities becomes especially important here. An agent should not simply inherit a human user’s entire authority. Organizations need ways to identify the agent, define its authority, record its actions, and revoke access when necessary.
Human Approval for High-Risk Actions
Not every action should happen automatically. Sending a routine internal report is different from deleting production data. Buying an item is different from changing financial records. Deploying code is different from merely reviewing it.
High-impact actions should therefore use approval gates. The agent can prepare the action. A human or independent control can approve it before execution. This approach limits the damage caused by goal hijacking or unexpected model behavior.
Human approval also creates an important accountability layer. The goal is not to slow every workflow. It is to place friction where mistakes could become expensive or irreversible.
Continuous Agent Monitoring
Security teams need visibility into what agents actually do. AI agent monitoring should track important tool calls, identity changes, unusual API activity, sensitive data movement, failed authorization attempts, and abnormal workflows.
NIST published 2026 research arguing for continuous monitoring and updating because fixed AI guardrails cannot be assumed to remain robust against adaptive adversarial prompts.
Monitoring also helps with investigation. If an agent behaves unexpectedly, security teams should be able to reconstruct what information it received, which tools it used, what identity it operated under, and which actions followed.
Secure Tool and API Connections
Tools should have narrow permissions and strong validation. APIs should expose only the functions the agent actually needs. Sensitive operations should require additional authorization.
Developers should also review third-party tools and dependencies. AI supply chain attacks can target models, extensions, prompts, tools, repositories, and other components that agents trust. Google reported in 2026 that attackers were exploiting files and extensions within AI coding environments.
A secure agent therefore needs more than a secure model. It needs secure dependencies, trusted tools, controlled APIs, validated inputs, protected memory, and clear authorization boundaries.
How Businesses Should Prepare for AI Agent Attacks
Businesses should begin with visibility. You cannot secure agents you do not know about. Security teams should identify which agents are being used, who owns them, what data they access, which tools they can call, and which identities they use.
This becomes especially important as employees adopt AI tools outside formal IT processes. Shadow AI can create unknown data paths and permissions. Google’s March 2026 Mandiant report identified AI asset visibility and uncontrolled AI deployment as important security concerns.
| Business Question | Why It Matters |
|---|---|
| Which agents exist? | Finds unknown AI systems |
| Who owns each agent? | Establishes accountability |
| What can each agent access? | Reveals excessive permissions |
| Which tools can it use? | Identifies dangerous capabilities |
| What data does it process? | Finds privacy risks |
| Which identity does it use? | Enables access control |
| Can access be revoked quickly? | Limits incident damage |
Organizations should also test agents before giving them sensitive access. Testing should include prompt injection, unsafe tool use, data exposure, permission abuse, memory manipulation, and unexpected actions.
Most importantly, security should not stop after deployment. Agent behavior can change when models, tools, prompts, integrations, or external data change. AI agent risks therefore require continuous review.
The Future of AI Agent Security
The future of security will likely move from protecting models alone toward protecting complete agent ecosystems. That ecosystem includes models, prompts, memory, tools, APIs, identities, external data, users, and other agents.
NIST launched an AI Agent Standards Initiative in February 2026 to support secure and interoperable agent development. Its work reflects the growing need for standards around systems that can act autonomously across digital environments.
Agent identity will become particularly important. When software can act on behalf of people, organizations need to know exactly which agent acted, under whose authority, with which permissions, and against which resources.
At the same time, defenders will increasingly use AI themselves. Google introduced AI-powered security capabilities in 2026 that focus on continuously identifying and responding to threats.
That creates an interesting security race. Attackers can use automation to move faster. Defenders can use automation to improve detection and response. The organizations that understand their AI systems clearly will have a stronger foundation for managing that race.
AI Agent Security FAQ
Are AI agents a cybersecurity risk?
Yes. AI agents can create additional security risks because they may access data, use tools, call APIs, maintain memory, and perform actions. OWASP identifies prompt injection, tool abuse, data exposure, excessive autonomy, memory poisoning, and cascading failures among the important risks.
The level of risk depends heavily on the agent’s design. An agent with limited read-only access has a smaller potential impact than one connected to sensitive systems with broad permissions.
Can hackers use AI agents to launch attacks?
Yes. Current 2026 threat intelligence has documented threat actors using agentic AI workflows for tasks such as reconnaissance, vulnerability validation, and credential harvesting. Google Threat Intelligence has reported these developments as part of the wider evolution toward more automated adversarial AI.
However, this does not mean every AI agent is an attack tool. Most legitimate agents have different purposes and security controls. The key concern is how much authority the system receives.
What is the biggest security risk with AI agents?
There is no single risk that applies equally to every deployment. The most serious situations often combine untrusted content, sensitive information, powerful tools, and broad permissions.
For example, an agent that can read private documents and communicate externally needs stronger controls than an agent that only summarizes public information. Security teams should therefore assess the entire workflow instead of focusing on one isolated vulnerability.
How can businesses secure AI agents?
Businesses should combine AI access control, least privilege, strong identity, monitoring, secure tools, input validation, and human approval for high-impact actions.
They should also test agents regularly. NIST and OWASP both emphasize that traditional security practices remain useful but must be adapted to the unique behavior and architecture of agentic systems.
Are autonomous AI agents safe to use?
Autonomous agents can be useful when organizations control their permissions, tools, data, and operating environment. Safety depends on architecture rather than the word “AI” alone.
A well-designed system should limit sensitive actions, monitor behavior, protect credentials, validate external content, and provide a way to stop or revoke the agent quickly. More autonomy should come with stronger controls.
Conclusion
The rise of autonomous agents is changing the cybersecurity equation. AI systems are no longer limited to producing text. They can interpret information, select tools, access systems, and complete multi-step tasks.
That creates real benefits. It also creates new opportunities for attackers. AI agent security must therefore cover more than the underlying model. It must protect identity, permissions, tools, APIs, memory, data, external content, and agent-to-agent communication.
The 2026 threat landscape already provides evidence of this shift. Google has documented agentic workflows in real threat activity. NIST is developing security guidance and standards for AI agents. OWASP is building practical security guidance around agent-specific risks.
For businesses, the message is practical. Know which agents you use. Limit what they can access. Monitor what they do. Test them against hostile inputs. Require approval for dangerous actions. Most importantly, treat every new agent as a software system with real security consequences.
Autonomous AI is moving quickly. Cybersecurity needs to move with it.
Article Related Information
| Sources | Explore now |
|---|---|
| AI Agents in 2026: What Are AI Agents and How They Will Change Work, Business, and Daily Life | Learn now |
| Agentic AI in 2026: How Autonomous AI Systems Will Transform Business, Software, and Human Work | Learn now |
| AI Agent vs Software Agent: Key Differences, Examples, and Use Cases Explained | Learn now |
| Types of Software Agents: A Complete Guide to Intelligent Software Agents | Learn now |
| AI-Powered Cybersecurity: How Artificial Intelligence Is Changing Online Security in 2026 | Learn now |
| OpenAI AI Agent Warning: What You Need to Know About AI Agent Security | Learn now |
| AI Workflow Automation in 2026: How Smart AI Workflows Are Transforming Business Productivity | Learn now |
| Generative AI in 2026: How Advanced AI Models Are Transforming Business, Creativity, and Everyday Life | Learn now |
Meta Description
Discover AI Agent Security in 2026. Learn how autonomous AI is changing cyberattacks, prompt injection, data theft, agent risks, and modern cybersecurity defenses.
3 Comments